 Indonesia denies foreign claim to rescued orangutans
 Turkey hosts COP31 climate talks in Antalya.
 Pope meets Argentine bishops.
 APOD: 2026 November 8 – Major Fireball Meteor
 Indonesian Horror Hit ‘Pabrik Gula’ Gets 2028 Sequel as MD Entertainment Lines Up Three Imax Films
North Korean Hackers May Have Stolen Billions. It Wouldn’t Be Their First Heist.
**
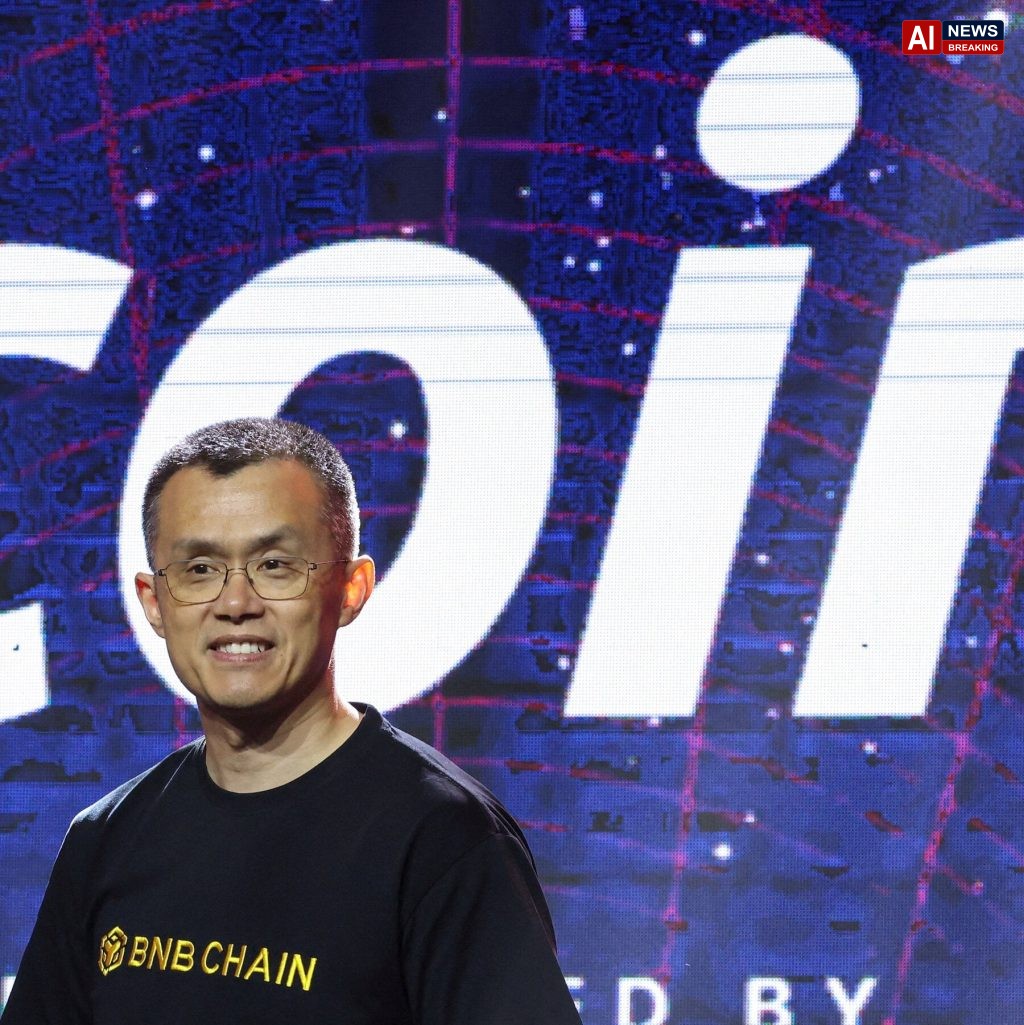
North Korean Hackers May Have Stolen Billions. It Wouldn’t Be Their First Heist. - AI News Breaking
north korean hackers have:
North Korean Hackers May Have Stolen Billions. It Wouldn’t Be Their First Heist The recent $6.3 billion theft from Binance, one of the world’s largest cryptocurrency exchanges, has sent shockwaves through the global crypto market. Analysts say the sheer scale of the breach, which saw a hacker siphon off 2.3 million USDT, underscores a growing threat to digital asset platforms..
While the identities of the perpetrators remain unverified, many experts point to the North Korean cyber unit, the Ministry of State Security, as a likely culprit. The country has a documented history of state‑backed cyber operations aimed at generating revenue and destabilising adversaries. North Korea’s cyber arsenal has evolved rapidly over the last decade..
Since 2014, the state‑run Lazarus Group has been linked to a series of high‑profile attacks, from the Sony Pictures hack to the WannaCry ransomware outbreak. These operations often involve sophisticated phishing schemes, malware, and zero‑day exploits. The group’s recent focus on cryptocurrencies is part of a broader strategy to circumvent sanctions and raise funds for the regime’s strategic initiatives..
Their capabilities are now recognised as a global security concern. The Binance breach shares several hallmarks of Lazarus Group tactics. Investigators noted the use of a custom banking trojan that bypassed two‑factor authentication, a technique that Lazarus has employed in past campaigns..
Additionally, the attackers exploited a misconfigured API key, a mistake that Lazarus has repeatedly made in earlier thefts. The parallelism in method and target suggests a deliberate link, though definitive proof remains elusive. Cryptocurrency exchanges have been particularly vulnerable to state‑sponsored attacks..
The anonymous nature of digital wallets and the relatively lax regulatory frameworks in many jurisdictions provide a fertile ground for illicit activity. Binance, which reportedly holds over $30 billion in customer funds, is a lucrative target for any adversary looking to maximise impact. The $6.3 billion loss is the largest recorded theft in the crypto sector, eclipsing previous high‑profile incidents such as the 2019 hack of Coincheck..
The impact on the global crypto market has been swift. Bitcoin fell by 6 % in the immediate aftermath, while Ethereum and other major altcoins saw double‑digit drops. Exchanges worldwide have tightened security protocols, with some pausing withdrawals and halting new account registrations..
Regulators in the United Kingdom and Singapore have urged firms to adopt multi‑layered authentication and real‑time transaction monitoring to mitigate similar threats. In a statement released Thursday, Binance’s CEO emphasized the company’s commitment to customer protection. “We have launched an independent forensic investigation and are working closely with law enforcement agencies to identify the perpetrators,” the CEO said..
The firm also announced the deployment of new security measures, including hardware‑based key storage and behavioural analytics. Despite these steps, some industry observers warn that the attack could erode consumer confidence in crypto exchanges for months to come. North Korean involvement in cybercrime is not a new story..
In 2017, the Lazarus Group allegedly stole $1 billion from the Central Bank of the Philippines via a series of complex phishing and malware attacks. That operation demonstrated the group’s ability to infiltrate highly secure financial institutions and exfiltrate large sums. More recently, a 2022 incident saw the group target a major U.S..
hedge fund, resulting in a $2.5 million loss. These cases illustrate the regime’s persistent strategy of using cyber operations as an alternative revenue stream. The international community has responded with a mix of diplomatic pressure and targeted sanctions..
Treasury Department has added several Lazarus Group affiliates to its sanctions list, freezing assets and restricting access to the global financial system. The United Nations has also imposed sanctions on North Korea’s cyber units, calling them “criminal enterprises that threaten global security.” However, enforcement remains challenging, as perpetrators often operate through shell companies and offshore servers. Security experts advise that the Binance theft may be only the latest in a long line of cyber heists by North Korea..
The regime’s sophisticated cyber capabilities, combined with its financial need, create a potent mix for future attacks. Financial institutions and crypto exchanges are urged to adopt zero‑trust architectures and continuous monitoring to detect anomalies before funds can be transferred out. Failure to do so could invite further large‑scale thefts that threaten the stability of the digital economy..
The fallout from the Binance hack will likely reverberate beyond the crypto sector. International law firms are already preparing for a wave of litigation from affected investors. Meanwhile, regulators are under pressure to tighten oversight of digital asset platforms, potentially introducing stricter capital requirements and mandatory insurance schemes..
The debate over how best to protect consumers without stifling innovation is already heating up. In conclusion, the $6.3 billion theft from Binance marks a watershed moment in cybercrime, spotlighting the threat posed by state‑backed actors such as North Korea’s Lazarus Group. As the world watches the investigation unfold, the need for robust cybersecurity measures and coordinated international response grows ever more urgent..
The incident serves as a stark reminder that the digital frontier, while offering unprecedented opportunities, also opens new avenues for large‑scale financial crime..
Updated: October 31, 2026
The Binance breach forces a reckoning: crypto’s very appeal—borderless, unregulated—has turned it into a state‑backed ransom vault, compelling regulators to pivot from laissez‑faire to a hard‑edge security posture or risk the sector’s collapse. In the long run, this event may trigger a regulatory clampdown that could stifle innovation unless a new, globally enforceable cyber‑security standard is forged, lest state actors continue to weaponize the digital economy for strategic gain