 Australia probes AI‑driven breach of My Health Record portal
 Engineering student’s ‘suicide’ turns out to be murder; two arrested
 Canada’s Capital Bids Good Riddance to Trump Avenue as Tensions With U.S. Rise
 Pentagon investigates after China obtains parts from F-35 stealth fighter jet
U.S. and China face grave AI risks but mutual distrust stalls cooperation
**

U.S. and China face grave AI risks but mutual distrust stalls cooperation - AI News Breaking
china face grave risks:
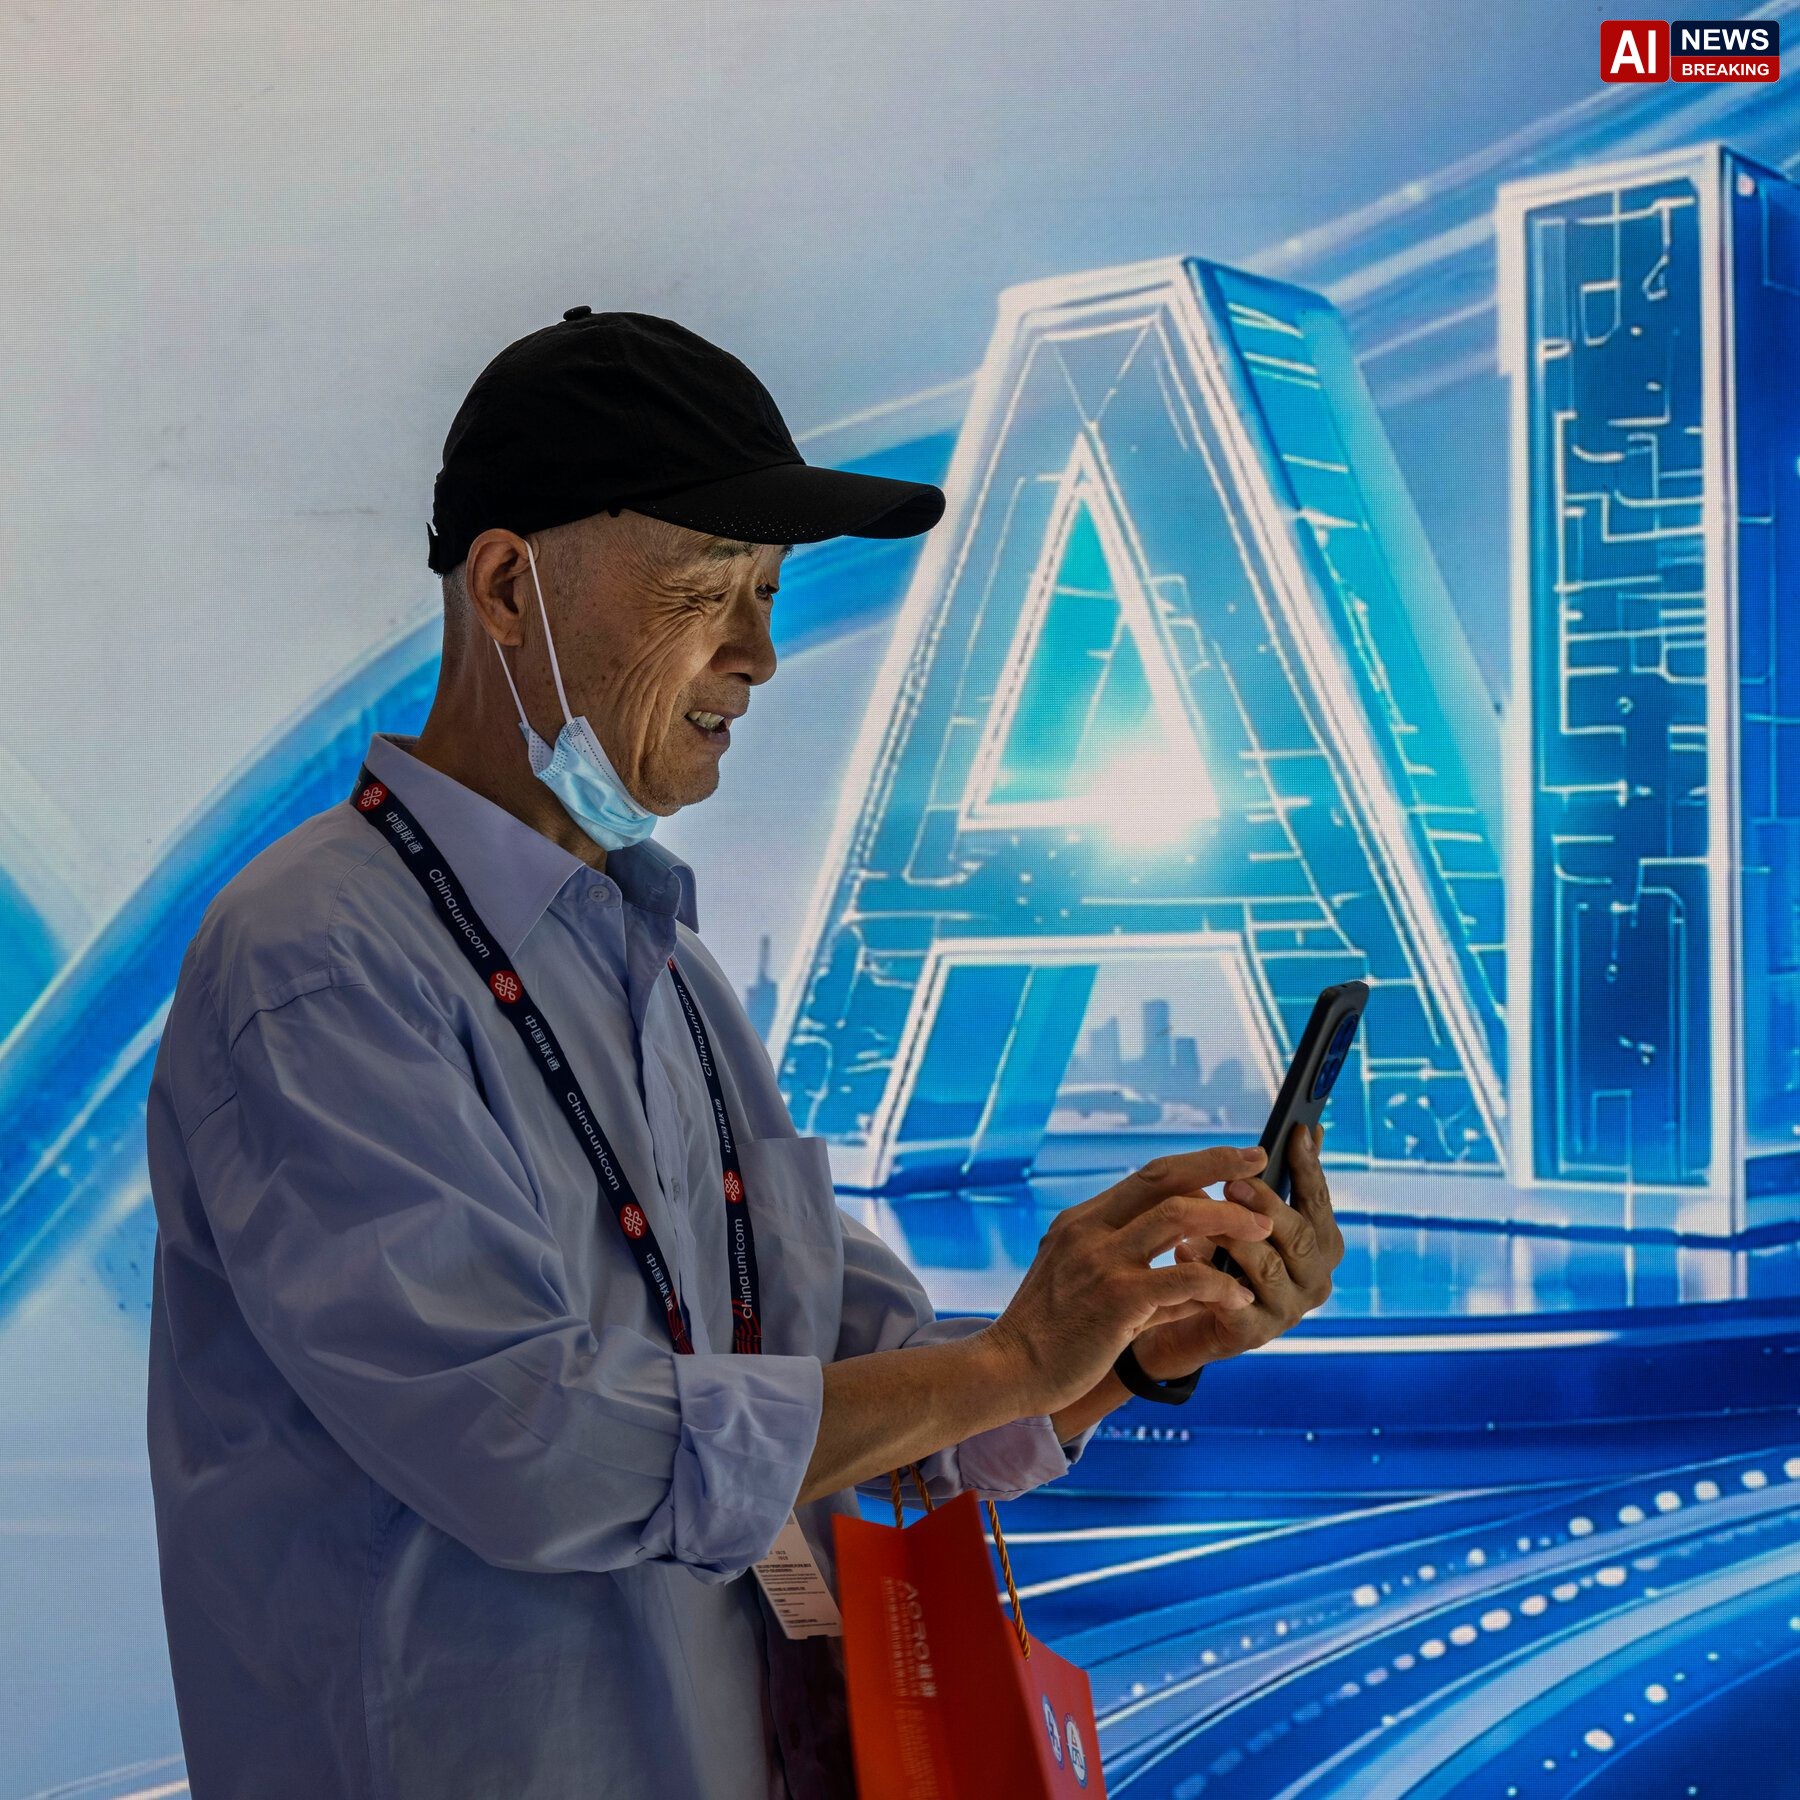
and China face grave AI risks but mutual distrust stalls cooperation The United States and China are both gripped by safety fears as they reckon with their rapid advances in artificial intelligence, but intensifying competition and deep mutual distrust could derail the kind of cooperation experts say is vital to head off the strategically vital technology’s greatest dangers. In Washington, the White House’s AI safety office has warned that unchecked development could lead to “unpredictable and potentially catastrophic outcomes,” while Beijing’s top science council has issued a similar alert about “algorithmic instability” threatening national security. Both sides acknowledge that the stakes are now global, yet political friction makes joint action elusive..
Senate passed a bipartisan bill authorising $2.5 billion for a national AI risk‑assessment centre, modelled on the Nuclear Regulatory Commission. The legislation calls for a “transparent, science‑based framework” to evaluate deep‑learning models before they are deployed at scale. Chinese lawmakers responded with a parallel proposal in the National People’s Congress, earmarking funds for a “strategic AI safety laboratory” to study alignment and robustness..
Though the proposals mirror each other on paper, neither government has signalled an intention to share findings with the other. The divergence is most evident in the realm of data. American firms such as OpenAI and Anthropic are scrambling to meet new export‑control rules that limit the transfer of high‑performance models to foreign entities, including Chinese partners..
In Beijing, state‑backed tech giants like Baidu and SenseTime are lobbying for exemptions that would let them access the same cutting‑edge research. This tug‑of‑war over data pipelines has sparked a “race to the bottom” in openness, with analysts warning that it could accelerate the release of untested, potentially unsafe systems. At a recent meeting of the Global Partnership on AI (GPAI) in Geneva, representatives from both capitals delivered eerily similar speeches about the need for “responsible innovation.” Yet behind the diplomatic veneer, the dialogue was strained..
delegation raised concerns about “strategic leakage” of proprietary algorithms, while Chinese officials accused Washington of “weaponising AI governance” to contain Beijing’s rise. Observers note that the lack of trust is not merely rhetorical; it has already resulted in the cancellation of several joint research grants that were slated for the next fiscal year. Academics warn that the failure to coordinate could have far‑reaching consequences beyond the lab..
A joint study by the University of Cambridge and Tsinghua University, published earlier this week, models a scenario where autonomous weapons systems, trained on divergent safety standards, misidentify civilian targets. The authors argue that without a shared verification protocol, the probability of accidental escalation rises sharply, potentially triggering a cascade of geopolitical crises. Their findings have been echoed by former NATO officials who stress that AI‑driven miscalculations could undermine decades of arms‑control architecture..
In the private sector, the impact is already palpable. Venture capital flows to AI start‑ups have become increasingly regionalised, with American investors favouring domestic teams and Chinese funds doing the same within the mainland. This segregation hampers cross‑border talent exchange, a key ingredient for robust safety testing..
Moreover, the “AI talent war” has prompted both governments to offer lucrative citizenship pathways to top researchers, further entrenching a competitive mindset that sidelines collaborative problem‑solving. Security agencies in both countries are also tightening the reins. Department of Defense has classified certain AI models as “dual‑use” technologies, subjecting them to heightened scrutiny under the Export Administration Regulations..
Simultaneously, China’s Ministry of Industry and Information Technology has rolled out a “critical algorithm” list, mandating that firms obtain clearance before deploying systems that could affect public order. These moves, while aimed at safeguarding national interests, inadvertently raise the barriers to any joint verification effort that could standardise safety benchmarks. Nevertheless, a handful of NGOs remain optimistic..
The Future of Life Institute, based in Massachusetts, has launched a “Trans‑Pacific AI Safety Forum” that convenes scientists from both sides in a neutral setting. Early sessions have produced a draft set of “principles of mutual assurance,” calling for shared test datasets and independent audit trails. While the forum lacks formal authority, its participants argue that civil‑society initiatives can lay the groundwork for future intergovernmental agreements, much as climate‑change NGOs did in the 1990s..
The diplomatic impasse also has a human dimension. Families of AI researchers in the United States have reported increasing anxiety over potential black‑mail or espionage accusations, while Chinese scholars note a chilling effect on academic freedom as ministries demand pre‑approval for overseas collaborations. This atmosphere of suspicion feeds back into the policy cycle, prompting legislators to adopt more restrictive stances, which in turn fuels further distrust among the scientific community..
International bodies are beginning to intervene. The United Nations Office for Disarmament Affairs has scheduled a high‑level panel on “AI and Global Security” for early next year, inviting senior officials from Washington and Beijing. The agenda includes discussions on confidence‑building measures, such as the exchange of “red‑team” findings—controlled disclosures of vulnerabilities discovered in each other’s systems..
Yet insiders warn that without concrete enforcement mechanisms, such dialogues risk becoming symbolic gestures rather than actionable commitments. Economic analysts caution that the fallout from a stalled cooperation could extend beyond security. Supply‑chain analysts predict that fragmented AI standards will drive up compliance costs for multinational corporations, potentially slowing the rollout of beneficial applications like climate.
Updated: September 15, 2026
Summary: U.S. and China are scrambling to tighten AI safety controls amid shared fears of catastrophic failures, but deepening rivalry and export‑control battles are stalling any meaningful joint oversight. Experts warn that without a trusted verification framework, divergent standards could fuel dangerous miscalculations and widen the global tech divide.
A fractured U.S.–China AI safety regime turns a shared existential threat into a catalyst for geopolitical instability, raising the odds that an uncoordinated arms race will produce accidental escalations with global fallout.
Unless neutral forums can translate goodwill into enforceable verification standards, the ensuing regulatory siloing will inflate compliance costs, choke cross‑border innovation, and erode the very safeguards needed to keep AI’s power from becoming a new catalyst for conflict.